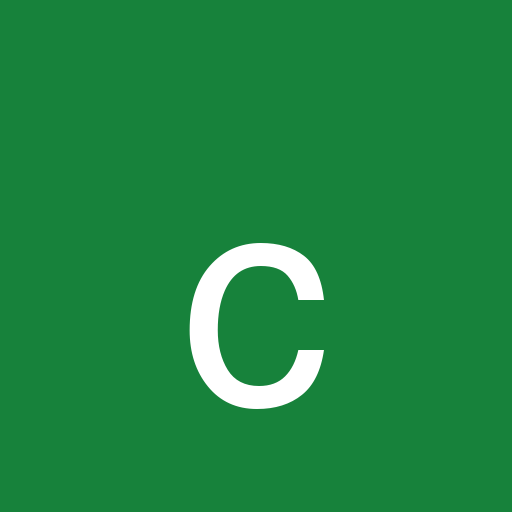
What chmod 660 means
The owner and group digits are both 6, combining read (4) and write (2). The other-user digit is 0, and no class receives execute permission. A regular file appears as -rw-rw----. Its owner and assigned group can open and modify it, while users outside that group cannot read, change, or run it.
The absence of execute permission identifies the item as data rather than a program. Mode 660 is generally unsuitable for directories because directories need execute permission for traversal. A shared file can use 660 inside a separately configured group-traversable directory.
Collaborative data, logs, and process files
A team can use 660 for a data file that several members must edit without exposing it to every account on the system. Applications can use the same pattern when two trusted processes share a group and both need to update a database export, queue state, or another non-executable working file.
Log and Unix socket permissions are often created by a service rather than maintained manually. Configure the service, its umask, or its socket settings so the desired owner and group mode persists after restart or rotation. A one-time chmod may be overwritten the next time the service recreates the file.
660 compared with 664
Mode 664 grants the same owner and group read-write access but also lets every other local user read the file. That can be reasonable for non-sensitive shared content. Mode 660 closes the file to users outside the assigned group, which is safer for private team data, internal logs, and application state.
Before selecting either mode, verify the file group and the accounts that need write access. If only one person or process should edit the file, chmod 600 is the narrower choice. Do not add group write access as a substitute for correcting mistaken ownership.
660 compared with shared directory modes
Mode 770 gives owner and group read, write, and execute permissions while excluding other users. Its execute bits suit a private shared directory or an intentionally executable file, not ordinary data. Applying 770 to a database or log adds execution capability with no benefit.
For a team directory that remains readable and traversable by other users, chmod 775 provides the directory execute bits and controlled group write access. Configure the directory and the files inside it separately: the container may use 775 while non-executable shared files use 660.